Solutions by Use Case
Active Threat Response
An active threat moves on information that is already available. 360 Privacy works to reduce that exposure and the risk surrounding it.
The Solution
How We Can Help
An active threat draws on two bodies of information: what a bad actor already holds and what remains publicly obtainable. 360 Privacy begins by assessing what is currently discoverable about the principal and anyone covered in the principal’s ecosystem, then concentrates removal and suppression on the records most relevant to the threat while monitoring search engines, social media, forums, and dark web sources for new exposure.
What an Active Threat Looks Like
What to Expect
Two fronts, one response
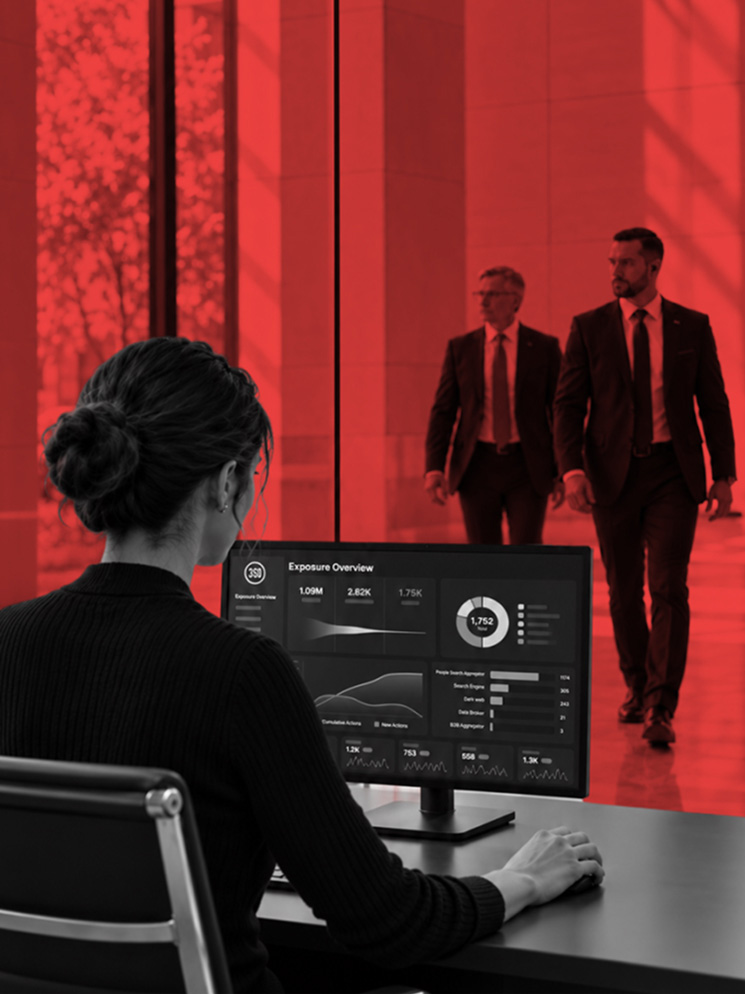
Physical and digital protection should operate in parallel. Executive protection, corporate security, legal, and law enforcement teams address the immediate threat, while 360 Privacy works the digital periphery, reducing the information that can be used to identify, locate, or target the principal.
Some exposure cannot be removed. We act within the confines of the law and what each source allows, then work with you directly on the risk that remains. This typically includes:
What We Do
Responding to an Active Threat
Immediate Exposure Assessment
Every source holding information on the principal and household is checked against what a bad actor would find today, which establishes what is already out and what is still discoverable.
Prioritized Suppression
Records tied to an active threat are targeted first. Search results are de-indexed while removal is pursued at the source, and upstream brokers are addressed so downstream sites stop repopulating.
Propagation Monitoring
Social platforms, fringe sites, forums, and breach repositories are monitored for the principal’s information as it spreads, including reposts and mirrored content.
Attribution Support
Managed cyber threat intelligence helps to identify the actor behind the activity and inform how the protective response is shaped.
Coordinated Escalation
Findings reach the Account Manager and the security team together, documented with the source, the data involved, and the action taken.
Sustained Coverage
Coverage continues after the event de-escalates. Records repopulate as brokers refresh their datasets, and actors have returned to the same targets months later.
Featured Resources
The Evolution of Doxing
Doxing has evolved from a simple act of exposure into a deliberate, multi-stage targeting operation with real-world consequences. The tactics have matured, the barrier to targeting has collapsed, and the response has to follow.
When Activism Crosses the Perimeter: Employee Activism and the New Risk Frontier
In late August, a group of protesters entered Microsoft’s Redmond headquarters and staged a sit-in inside the office suite of company president Brad Smith. The group, calling itself No Azure for Apartheid, livestreamed the action, unfurled banners, and demanded the company cut ties with Israel. Seven people were arrested. Two employees were later terminated for breaching …
When the Opt-Out Fails: Data Brokers, Assassination Culture, and the Rising Risk to Leaders
In June, a group of researchers from UC Irvine published a comprehensive audit of data brokers registered under the California Consumer Privacy Act (CCPA). The objective: test whether consumers could meaningfully exercise their legal right to opt out of data collection and sale. What they found is both alarming and somewhat validating: • Over 40% …
Frequently Asked Questions
Can’t find the answer you’re looking for? Reach out to our client support team.
Search results can be de-indexed quickly, which closes the fastest path to the record. Removal at the source runs on that source’s timeline and varies by site. Both tracks start at the same time rather than in sequence.
Dark web and forum content has no removal mechanism, no opt-out, and no compliance process. What happens instead is full disclosure of what was exposed, monitoring for how far it spreads, and the protective steps that address what is now public.
Exposure reduction runs alongside them. The actor’s remaining access narrows, propagation is tracked as it happens, and every finding is documented with its source and data type for whoever needs the record.
Managed cyber threat intelligence supports attribution investigations, which helps to identify a bad actor and inform the response.
Get Started Today
Every point of data is a point of entry.
Discover how 360 Privacy can help reduce your exposure.